
ISO 27701 consultants in India
Extend your ISO 27001 system with privacy controls and give customers evidence of how you handle personal data. Based in Hyderabad, serving India and international clients.
- Practitioner-led
- Since 2013
- Hyderabad, India
What does ISO 27701 consulting involve?
ISO/IEC 27701 extends ISO 27001 with requirements for a privacy information management system (PIMS). AdWiser helps you define your role as controller or processor, map personal data, add privacy controls and records, align with GDPR and India's DPDP Act, and prepare for the certification audit.
- Standard
- ISO/IEC 27701 (privacy extension to ISO 27001)
- Who needs it
- Controllers and processors of personal data that already run, or are building, ISO 27001
- Delivery
- On-site visits across India, plus remote delivery
- Certificate issued by
- The accredited certification body you select, never by AdWiser
What we do
Privacy gap assessment
Compare your ISMS and privacy practice with the ISO 27701 requirements.
Data mapping and records
Records of processing, purposes, lawful basis and transfers.
Privacy controls and documents
Policies, notices, consent, rights handling and processor terms.
Audit readiness
Internal audit and certification-audit coaching.
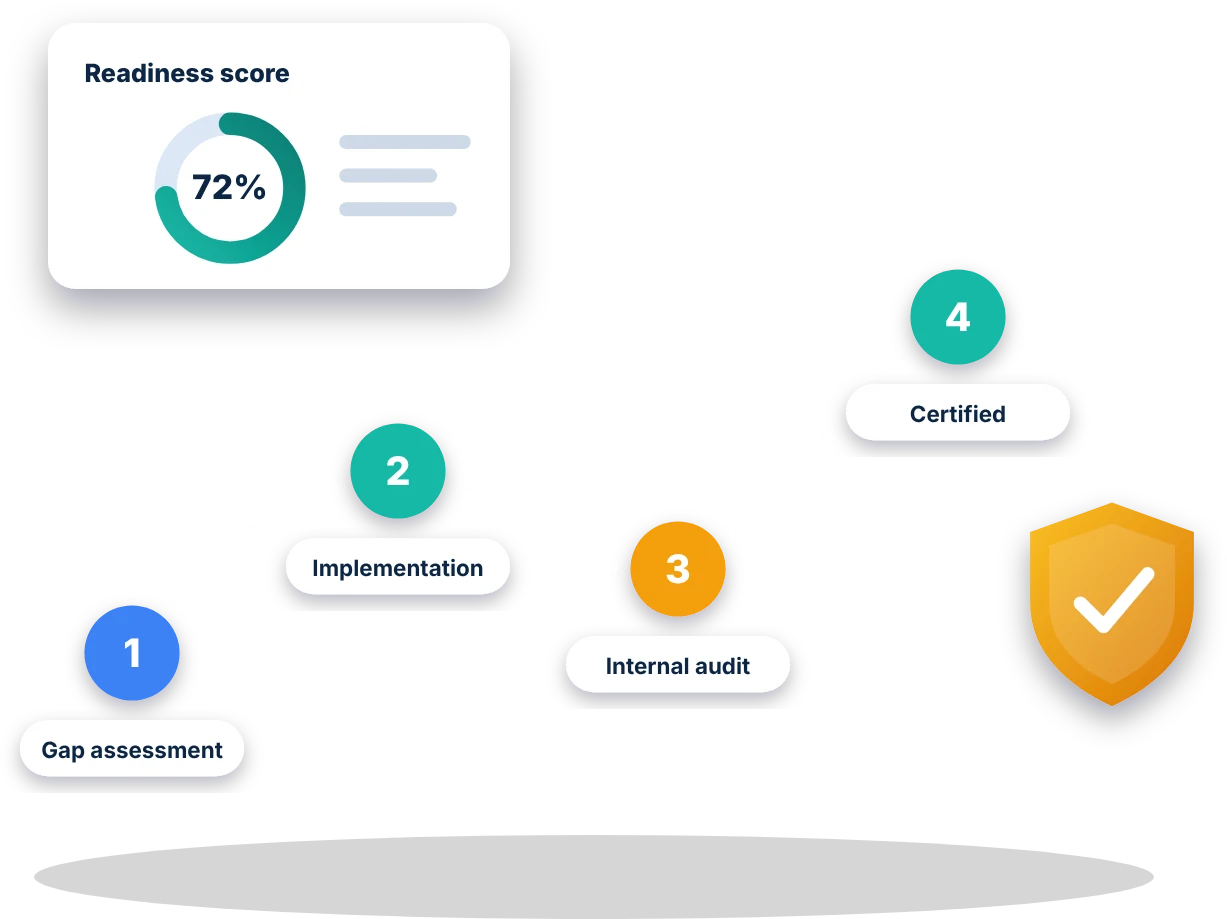
How an engagement works
- 1
Confirm ISMS base
Check your ISO 27001 system is ready to extend.
- 2
Map personal data
Roles, data, purposes, systems and transfers.
- 3
Build privacy controls
Add the PIMS requirements and records.
- 4
Check
Internal audit and management review.
- 5
Certify and sustain
Certification audit support and improvement.
Where we work
Our head office is in Miyapur, Hyderabad. We do not run branch offices: our consultants travel to your site, so you get the same team in any city.
Across India
- Hyderabad (head office)
- Bengaluru
- Chennai
- Mumbai
- Pune
- Delhi NCR
- Kolkata
- Ahmedabad
- Kochi
- Jaipur
- and every other city in India
International clients
We work remotely with organisations in Australia, Ghana, Nigeria, Mauritius, USA and Saudi Arabia.
Frequently asked questions
Do we need ISO 27001 first?
ISO 27701 is built as an extension of ISO 27001, so it is normally implemented with or after it. We can help you do both together.
Does ISO 27701 prove GDPR or DPDP compliance?
No standard replaces legal compliance. ISO 27701 gives a structured way to manage privacy and can support GDPR and DPDP work, but legal duties still need to be confirmed with your counsel.
Do you issue the certificate?
No. An accredited certification body issues it after auditing you.
Do you work outside Hyderabad?
Yes. We serve organisations in every city in India and work remotely with clients abroad.
Can we begin with a toolkit?
Yes. The ISO 27701 toolkit provides editable privacy templates, and consulting can be added where you need expert input.
Related articles
 ISO Standards
ISO 27701 Toolkit: What to Look For and How to Use It
An ISO 27701 toolkit can save weeks of drafting, but only if you adapt it to how your organisation really handles personal data. This guide covers what to look for, how to use it and where it falls short.
19 Nov 2026 · 6 min readRead → ISO Standards
What Documents You Need for ISO 27701:2019 Implementation
ISO 27701:2019 extends ISO 27001 with privacy requirements, and the documentation extends with it. Here is a practical list of the documents and records you need, grouped by purpose.
17 Nov 2026 · 5 min readRead →Talk to our ISO 27701 team
Tell us your size, scope and timeline. We reply with a plan, not a sales script.
Talk to a consultant
Send your question and an expert will reply by e-mail or phone, usually within one working day.